
Phishing: What Is It and Why Does It Matter?
Phishing: What Is It and Why Does It Matter?
What phishing is, how attackers make malicious messages look convincing, the warning signs to watch for and what to do if somebody clicks.
Phishing is an attempt to trick someone into clicking, signing in, sharing information, sending money or taking another action that benefits an attacker. Email remains one of the most common routes, but phishing can also arrive through texts, phone calls and social media.
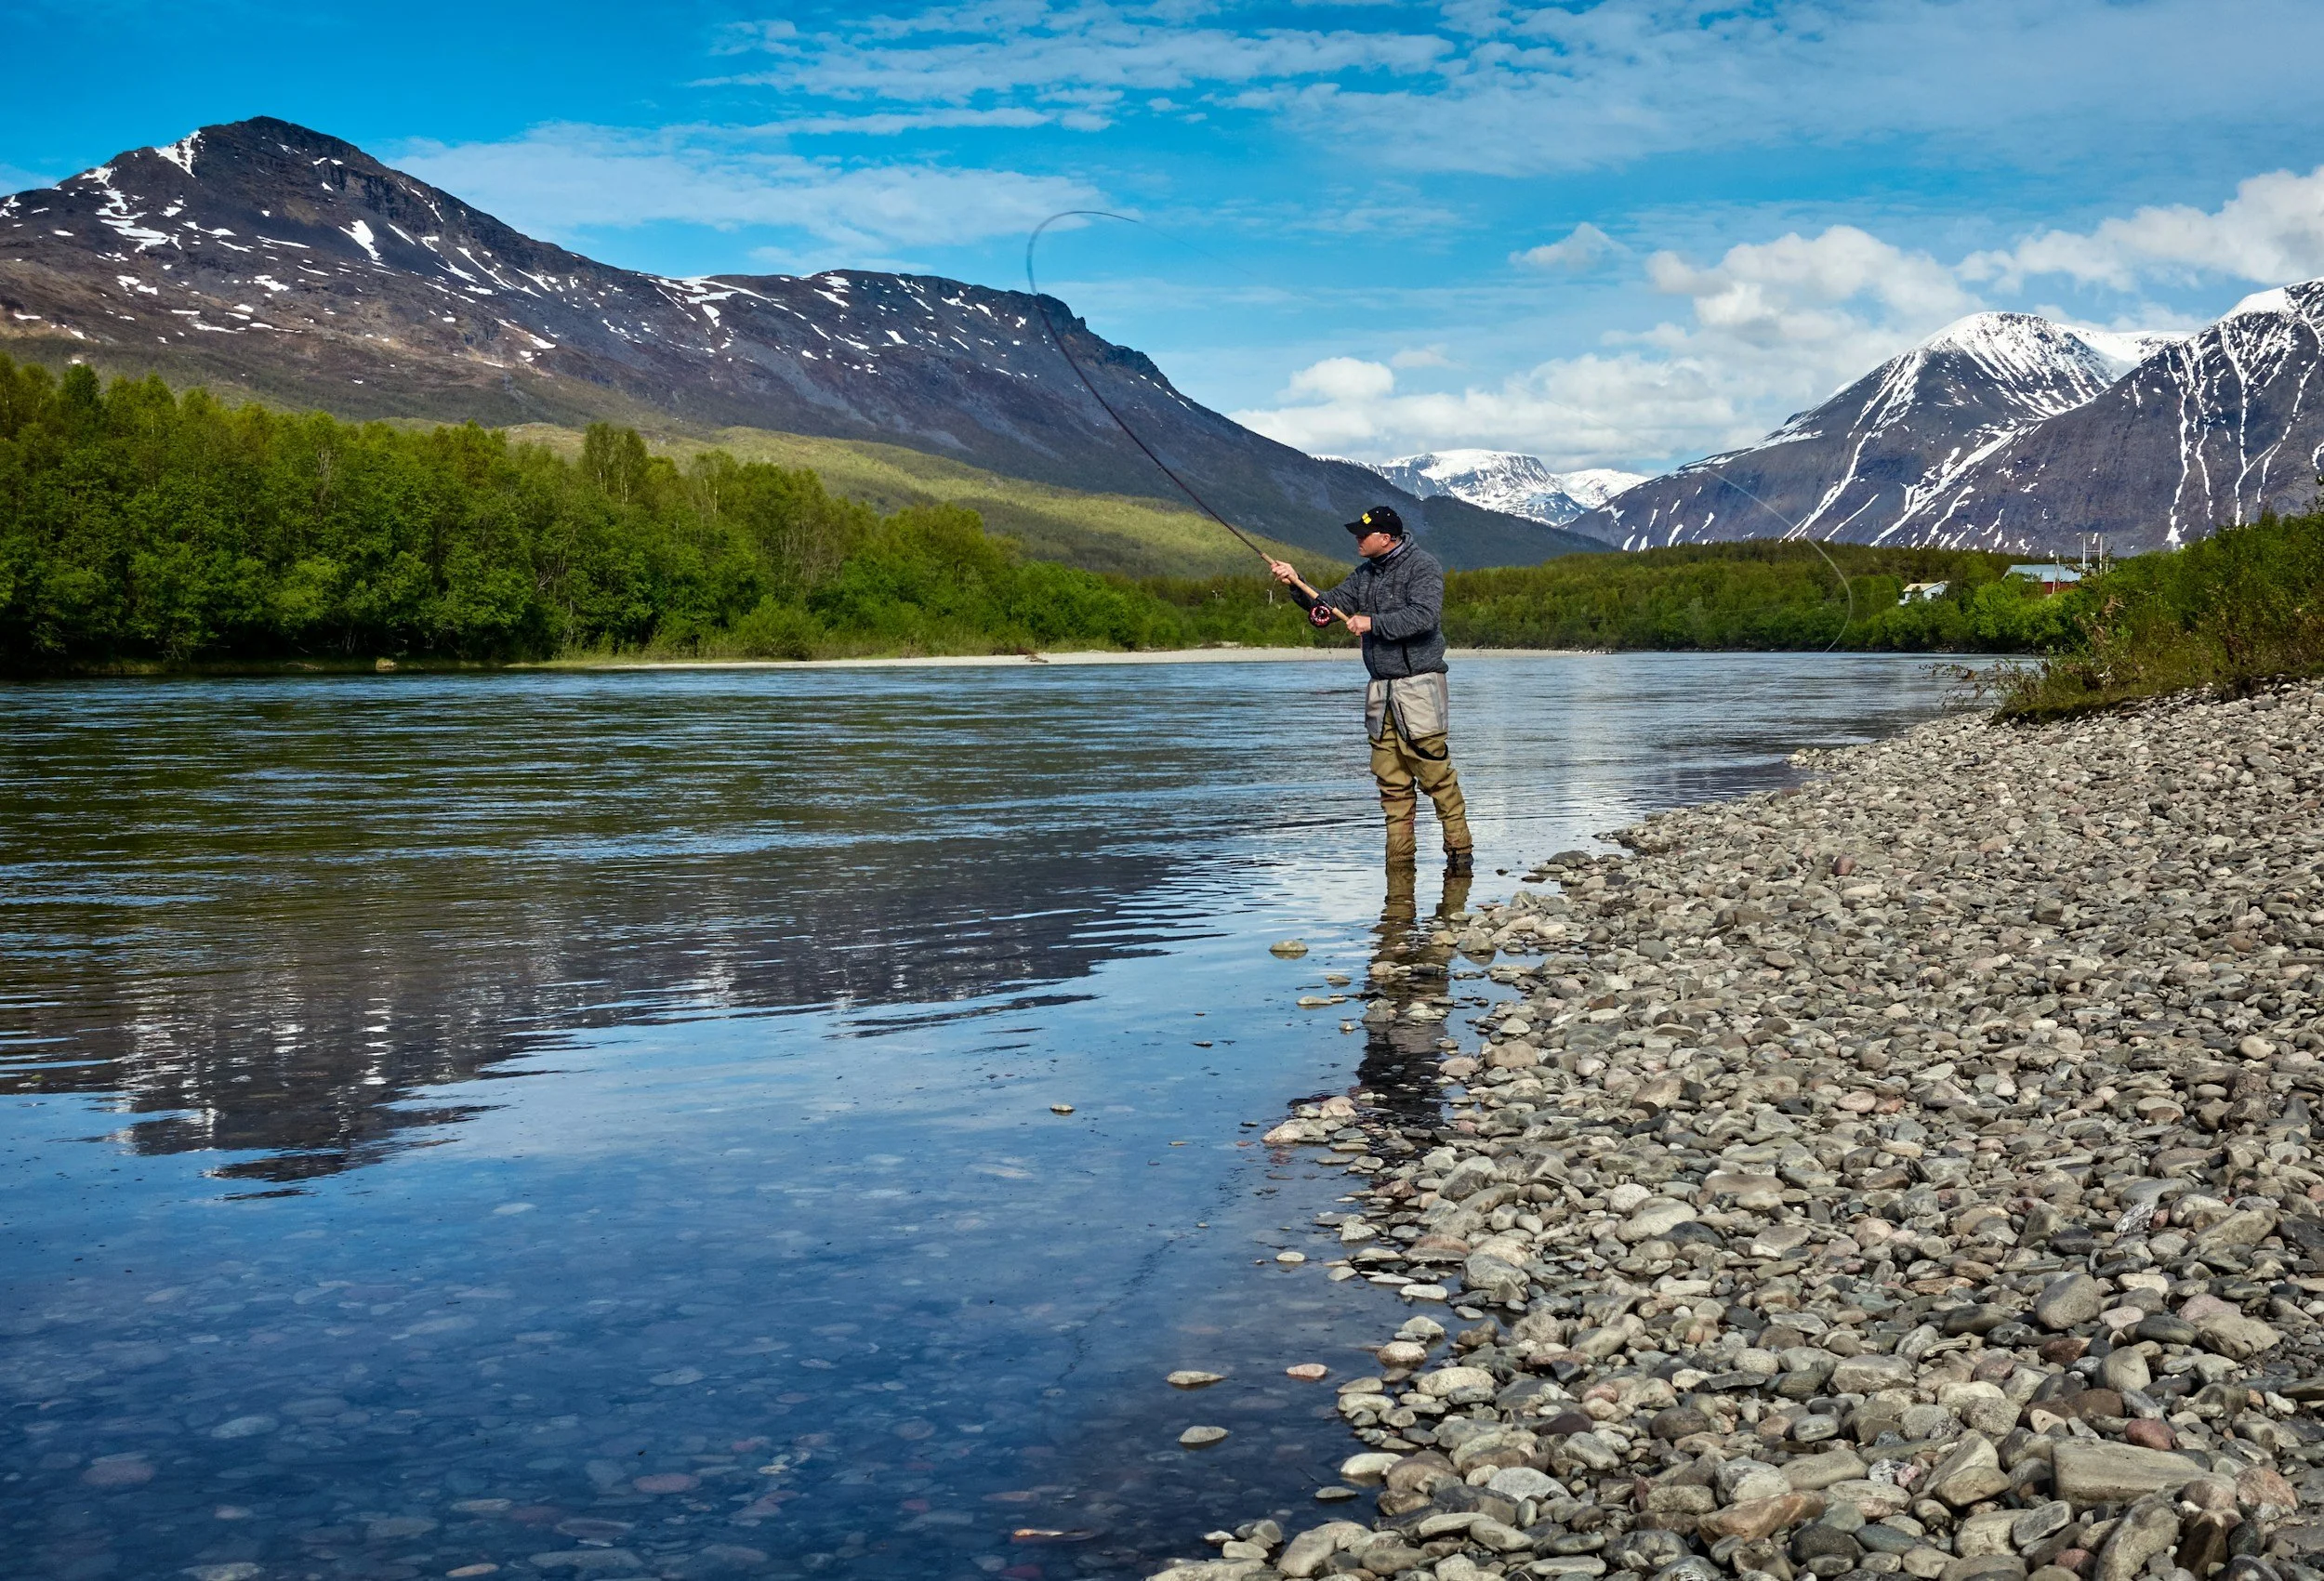
When you picture fishing, you may conjure up tranquil mental images of a little wooden boat on a peaceful lake with mountains sprawling throughout the surrounding areas. But phishing, on the other hand, is a far cry from such serenity.
By now, you've likely heard of phishing in some capacity; you may even know someone who's fallen victim to a successful attack. But what is it, what should you look out for, and what should you do if you get caught on the hook of a hacker?
What is Phishing?
In simple terms, phishing is when an attacker attempts to lure a user into doing - or clicking - on something that they want. Typically, this is in the form of a bad link that can install malware on their machine or direct them to a malicious website.
These days, attempts can occur via social media, text message or phone - however, the most common form of such attacks is through email. Usually, there aren't any specific targets with phishing attempts - a lot like actual fishing, the 'phishermen' (if you will) cast their bait into a general direction and hope for a nibble.
Once you're on the hook, they can install malware, sabotage your systems, or even steal intellectual property and money. Organisations of any shape and size aren't safe either - a simple Google search for 'phishing attacks' can attest to that.
Equally, there is a more targeted version of a phishing attack. Here, as the NCSC says, "the attacker may use information about your employees or company to make their messages even more persuasive and realistic", something that is referred to as spear phishing.
Why is it Relevant?
The ongoing conflict in Ukraine has led experts from Google's Threat Analysis Group (TAG) to issue a warning. A post on their site reads, "Government-backed actors from China, Iran, North Korea and Russia, as well as various unattributed groups, have used various Ukraine war-related themes in an effort to get targets to open malicious emails or click malicious links."
When a subject dominates headlines globally in such a fashion, it's only natural to expect to see relevant links, posts and emails about it. However, it's imperative to exercise caution on all levels when browsing online - or risk paying the price.
Things to Look Out For
Phishing attempts in their infancy were clear to spot - however, now they're getting increasingly harder to identify.
Cofense has put together a handy 10-step guide for things to look out for in a phishing attack. They are:
Unfamiliar tone or greeting
Pay attention when the language doesn’t fit the person or organisation supposedly contacting you.
Grammar and spelling errors
Unexpected errors can be a warning sign, particularly when combined with other suspicious behaviour.
Email, link or domain inconsistencies
Check whether the sender address and destination really belong to the organisation being represented.
Threats or urgency
Be wary when a message pressures you to act before you have time to check the request.
Suspicious attachments
Unexpected files should be treated cautiously, particularly when the sender or context feels unusual.
Unusual requests
A request that falls outside normal process deserves independent verification.
Short and sweet
Very brief messages can deliberately leave out context and push the recipient towards the requested action.
You didn't start the conversation
Be cautious when an unsolicited message unexpectedly asks you to open something or take action.
Requests for sensitive details
Credentials, payment details and personal information should never be handed over simply because an email asks.
See something, say something
Make it easy to report a suspicious message rather than expecting every employee to investigate it themselves.
How to Stay Safe
As mentioned earlier, phishing attempts can look indistinguishable from a genuine email. But the best form of defence is to be sceptical of everything that comes into your inbox.
The level of your defences - and optimising things such as 2FA - can be the difference between an incredibly costly phishing attack and a close call.
You should apply common sense and operate with more than an air of scepticism in some situations - for example, don't transfer a hefty sum of money because an email has asked you to. Pick up the phone and call your CEO or whoever is requesting the transaction and confirm it's genuine - or better yet, ask them in person. Hackers make a living out of exploiting people - don't be their next victim.
If you spot something that doesn't look right - or you know is a phishing attempt, report it to the NCSC.
What Happens if You Click on a Bad Link?
Sometimes, the worst can happen, and you might click on a malicious link. What should you do if this happens?
Report it immediately
Report it to the appropriate people within your organisation straight away. If you work with an MSP, alert them immediately, too. That way, they can be alert for any suspicious or unusual activity.
Consider sensitive access
If you have access to sensitive company information or financial accounts, they may be compromised. Contact your bank immediately and consider closing the account(s).
Watch your accounts
Equally, watch for any unauthorised charges appearing on your accounts.
Consider reporting it
Depending on the nature of your organisation, you should consider reporting the attack to your local police department.
If you're in England, Wales or Northern Ireland and have lost money - or been hacked by a phishing attack - visit Action Fraud or call 0300 123 2040. For those in Scotland, report it to Police Scotland by calling 101.
The Final Word
If you're worried that your network has holes that could be laid bare by a phishing attack, why not get in touch with an MSP such as Fifosys and hear more about how we can help?
With 24/7/365 defences and state-of-the-art monitoring, you can rest in the comfort of knowing that your systems are safe from malicious outsiders. We're only a phone call away.
Phishing FAQs
What is phishing?
Phishing is an attempt to trick someone into taking an action that benefits an attacker, such as clicking a malicious link, opening an attachment, entering credentials, sharing sensitive information or transferring money.
What is spear phishing?
Spear phishing is a more targeted form of phishing. Attackers use information about a person, employee or organisation to make the message more convincing and relevant to the intended recipient.
What are the common signs of a phishing email?
Warning signs can include unusual requests, unexpected urgency, suspicious attachments, inconsistent email addresses or links, requests for credentials or payment information and messages that do not fit the normal tone or process of the supposed sender.
Can phishing emails look completely genuine?
Yes. Modern phishing attacks can copy legitimate brands, use familiar business context and sometimes originate from compromised genuine accounts. That is why unusual or sensitive requests should be verified through a separate trusted channel.
Does two-factor authentication stop phishing?
Two-factor authentication makes stolen passwords less useful and is an important security layer, but it does not eliminate phishing risk. It should be combined with email protection, secure identity controls, user awareness and monitoring.
What should I do if I click a phishing link?
Report the incident immediately to your IT or security team or managed service provider. The organisation can then investigate the message, account activity and any systems or data that may have been exposed and take appropriate containment action.
How can businesses reduce phishing risk?
Businesses can combine email filtering, domain protection, strong authentication, limited permissions, security awareness, independent verification of sensitive requests, monitoring and a clear incident-reporting process.
Make phishing harder to turn into a breach
We can help you strengthen email security, identity controls, monitoring and response around one of the most common routes into a business.
Talk to our team
Bring us your email-security, identity or phishing concerns and we’ll help you understand where the gaps sit.
Security Framework
See how email protection, identity security, monitoring and response fit into a wider cyber security approach.